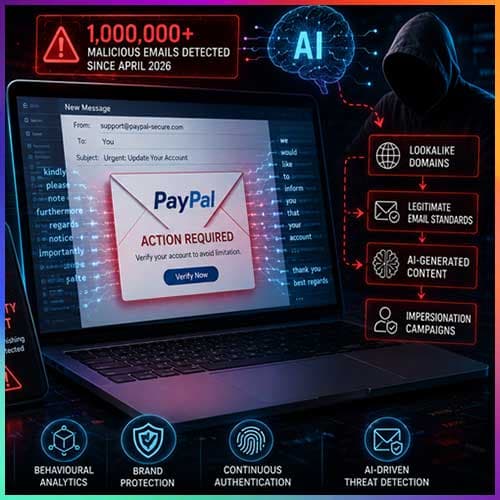
Cybercriminals are increasingly using text salting to bypass AI-powered email security, with researchers detecting more than one million malicious emails employing the technique since April 2026.
Instead of exploiting technical vulnerabilities, attackers are manipulating language by inserting AI-generated filler text and subtle variations that help phishing emails evade keyword-based detection systems.
The attacks have evolved beyond traditional phishing.
Threat actors are registering lookalike domains, authenticating them with legitimate email standards, and combining them with AI-generated content to create convincing impersonation campaigns.
As a result, these emails can pass authentication checks while appearing to originate from trusted brands.
The trend highlights a critical shift in cybercrime.
The challenge is no longer just verifying whether an email is technically authentic—it is determining whether the sender is genuinely authorized to represent the brand.
As AI-generated phishing becomes more sophisticated, organizations must move beyond traditional email security and adopt identity-centric, behavioural, and brand-protection technologies.
In the AI era, protecting digital trust has become just as important as protecting digital infrastructure.
MagazineCoverage
AI-Powered Email Attacks Bypass Security
Cybercriminals are increasingly using text salting to bypass AI-powered email security, with researchers detecting more than one million malicious
1 min read0 views